AIBOM Tools in 2026: Formats, Open-Source Projects and Vendor Platforms Compared
There are three ways to produce an AIBOM in 2026. First choose a format: CycloneDX ML-BOM (machine-learning-model + data component types; common in security/CI-CD tooling) or the SPDX 3.0 AI Profile (Linux-Foundation/ISO-rooted; often preferred for regulatory filings) — both stable and machine-readable. Then pick tooling: open-source generators (OWASP AIBOM Generator, cdxgen, operational-aibom, and repo/registry scanners that emit CycloneDX 1.6 ML-BOM + SPDX 3.0) for zero cost and full control; or commercial AI-SPM platforms (Manifest, Cisco AI Defense, and the AI-BOM features inside Orca, Wiz, Sysdig, Mend, Cycode) that treat the AIBOM as a living, continuously-enriched artifact with vulnerability and policy context. PlayCISO gives you the whole generate-validate-convert-diff workflow free. This post compares all three and tells you how to choose. Sources: CycloneDX; SPDX; OWASP Gen AI Security Project; vendor documentation.
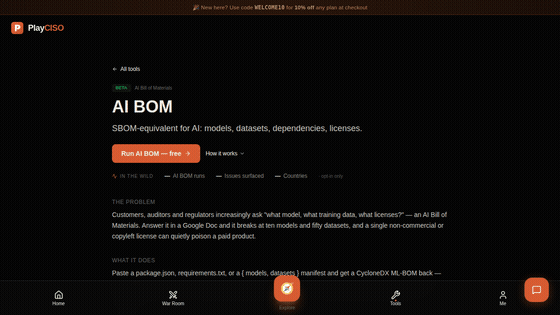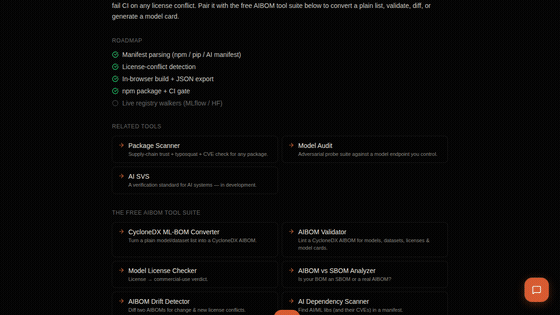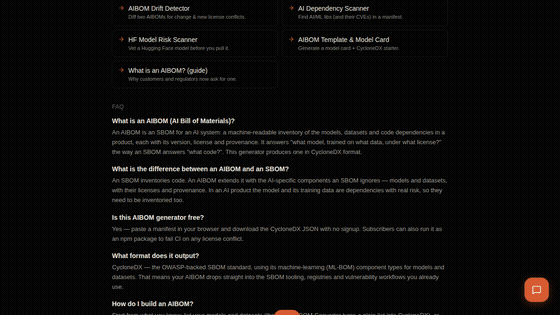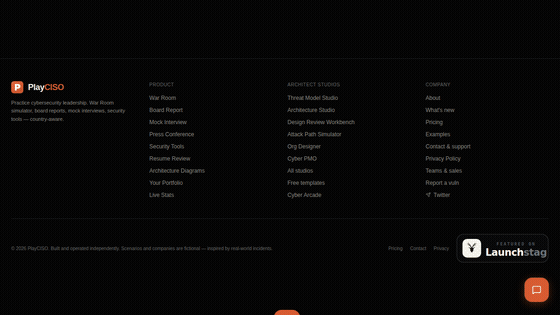
Producing an AIBOM (AI Bill of Materials) in 2026 comes down to three decisions: which format to emit, which tool generates it, and whether you need a platform to keep it alive. This compares the real options — formats, open-source projects on GitHub, and commercial vendors — and the free tools you can use today. For the fields each of these must capture, see the AIBOM parameters checklist; for the concept, what an AIBOM is and why it matters.
Step 1 — pick a format
Two standards dominate, both stable and machine-readable:
| CycloneDX ML-BOM | SPDX 3.0 AI Profile | |
|---|---|---|
| Models/data | machine-learning-model + data component types | AI Profile (model) + Dataset Profile |
| Strength | Security & CI/CD tooling; Dependency-Track | Model type, training, data handling, explainability, limitations, energy |
| Best for | Engineering / scanning pipelines | Regulatory filings & procurement (LF/ISO lineage) |
You do not have to choose permanently — convert between them with the free ML-BOM Converter →, and if you are still deciding between an AIBOM and a plain SBOM, the AIBOM vs SBOM tool → and our SBOM vs AIBOM vs MLBOM explainer lay out the difference.
Step 2 — open-source & GitHub tools
For zero cost and full control, the open-source ecosystem is strong:
- OWASP AIBOM Generator — extracts a Hugging Face model's metadata into a CycloneDX 1.6 AIBOM and scores its completeness with recommendations. The best place to learn which fields matter.
- cdxgen — the Swiss-army BOM generator across many languages and ecosystems, CI/CD-ready with automatic submission to Dependency-Track.
- Repo/registry AIBOM scanners — newer open-source scanners point at a repo, Git host, cloud account or Hugging Face model and emit a CycloneDX 1.6 ML-BOM plus SPDX 3.0 and a SARIF report, with no SaaS callback (search GitHub for "operational-aibom" and "AIBOM scanner CycloneDX SARIF").
- Adjacent: model safety — Protect AI's ModelScan checks a model file for unsafe code. Not an AIBOM generator, but the integrity/safety signal belongs in one.
- The specs themselves: CycloneDX Tool Center and SPDX.
Step 3 — commercial AI-SPM platforms
Vendors fold AIBOM into broader AI security posture management. They matter when you need AIBOMs as a living operational artifact across many products and suppliers — continuously generated and enriched with vulnerability, lifecycle and policy context, rather than a one-off file. Representative options (evaluate against your own stack; positioning per their documentation):
- Manifest — SBOM/AIBOM generation and management at scale, treating the AIBOM as a continuously-updated operational artifact with an AI-risk module.
- Cisco AI Defense — an AI-BOM view of your AI stack inside its AI-security platform.
- AI-BOM features inside cloud/app-security suites — Orca, Wiz, Sysdig, Mend and Cycode have published AI-BOM / AI-asset-inventory capabilities as part of their platforms.
The trade-off is the usual one: platforms buy you scale, continuous enrichment and policy workflow; open-source and free tools buy you control, zero cost and no data leaving your environment. Most teams start with the latter and adopt a platform when the operational load justifies it.
What you can do free on PlayCISO
You can run the entire generate → validate → convert → diff → licence-check workflow in the browser, free and no signup:
- AI BOM generator → — manifest to CycloneDX-style AIBOM with per-component licence risk.
- AIBOM Template → — a correct starting structure.
- AIBOM Validator → — structural + completeness check.
- ML-BOM Converter → — emit a CycloneDX ML-BOM.
- AIBOM Diff → — what changed between releases.
- Model License Checker → and AI Dependency Scanner → — the licence and dependency layers.
How to choose
- Just need a valid AIBOM today? Use PlayCISO's free tools or the OWASP AIBOM Generator / cdxgen. Emit CycloneDX ML-BOM for engineering, SPDX 3.0 AI Profile for a regulator.
- Filing for compliance? Prefer SPDX 3.0 AI Profile and keep the completeness score high (the parameters checklist is your guide).
- Managing dozens of products/suppliers? That is where a commercial AI-SPM platform earns its keep — continuous, enriched, policy-driven.
The format is a five-minute decision, the first AIBOM is a free one, and a platform is a problem for when you have scale. Start by generating one — then keep it honest with the parameters checklist and the build walkthrough.
Generate yours now with the free AI BOM generator, and follow AI supply-chain security in PlayCISO AI Labs. Comparisons reflect public standards and vendor documentation; evaluate any tool against your own requirements.
Ready to practise the decisions these articles describe?
Run a free War Room →